10. Borders, searches and coercion
The short version
- The border is a high-scrutiny zone. Several distinct UK powers let officers examine, scan, seize or retain devices, some without prior suspicion.
- Which power matters. A duty to co-operate under one power must not be assumed under another; ask which one is being used.
- Carry less. A quick manual look at what is visible is the common risk, so minimise what is on the device and switch off lock-screen previews.
- Biometrics are easy to compel in the moment. Use a long passcode and disable biometrics before you cross.
- After an inspection, tidy up: change key passwords, check logins, look for changes you did not make.
Legal status reviewed 1 August 2026. UK border device powers have different thresholds, purposes, duties, and safeguards. This page gives general information, not advice about whether to answer a question or unlock a device in a particular examination.
When theory meets force
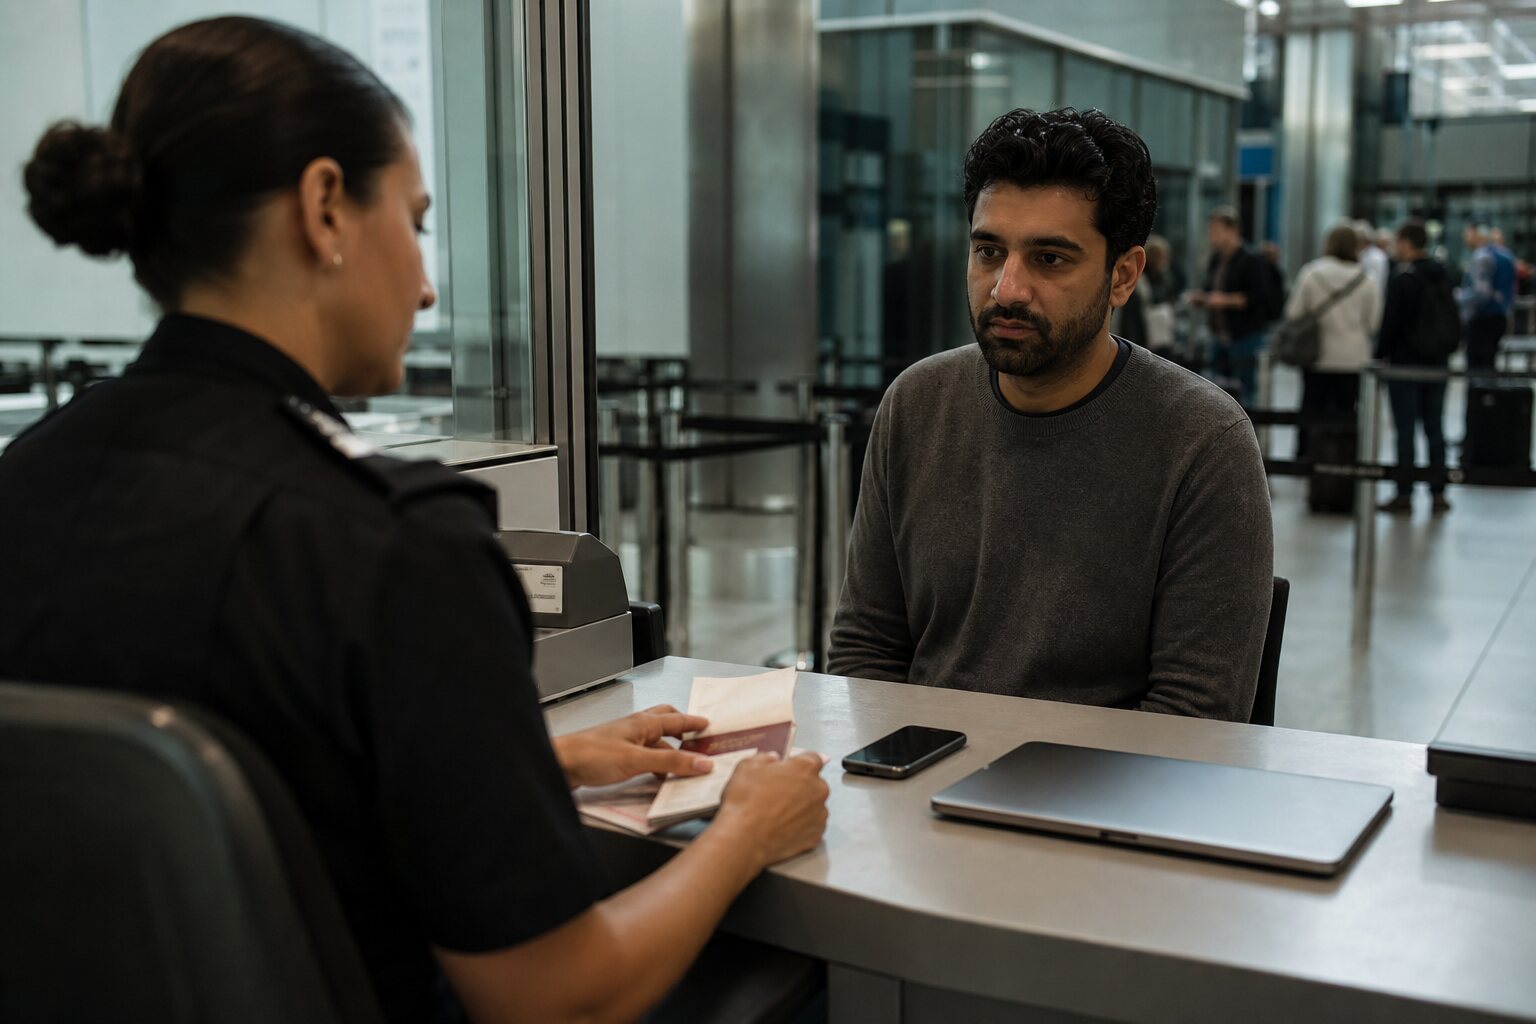
Border crossings are one of the few everyday places where the state can inspect devices in ways that would be unusual elsewhere.
The legal basis varies by country, but the practical reality is fairly consistent: officers can ask questions, request devices and make decisions quickly. This is not an abstract privacy debate. Compliance, delay, refusal or a misunderstanding can all have consequences.
The right response depends on context:
- the country you are entering;
- your citizenship status;
- the purpose of travel.
In the UK, officers have several distinct legal routes to examine, scan, search, seize or retain electronic devices. Some need no warrant or prior suspicion; others need reasonable grounds tied to a defined purpose. A duty to co-operate under one power must not be assumed under another.
That does not mean every traveller is searched. It means your privacy plan should treat the border as a high-scrutiny environment, and any legal conclusion has to identify the power actually being used.
Which UK power is being used?
Three quite different regimes, in brief:
- Schedule 7 / Schedule 3 (national security). Schedule 7 to the Terrorism Act 2000 permits examination at ports and borders to determine whether a person appears to be involved in terrorism, with no requirement for prior suspicion. Schedule 3 to the Counter-Terrorism and Border Security Act 2019 provides a related regime for hostile activity.
- 2025 immigration device power (narrow). Under the Border Security, Asylum and Immigration Act 2025; applies only to a defined "relevant person" who arrived without the required permission.
- 2026 targeted scan power (child abuse images). Section 84 of the Crime and Policing Act 2026; a required scan, not a general search.
Schedule 7 and Schedule 3 are both UK-wide and subject to statutory codes and safeguards. Wilful failure to comply or obstruction can be an offence. These are exceptional national-security powers, not a general rule that any border officer may search any phone for any purpose.
The 2025 Act power is narrower. It applies only to a "relevant person" who has entered or arrived without the required leave, clearance or travel authorisation and has not since received leave. An authorised officer must have reasonable grounds to suspect the device may contain information relating to specified facilitation offences.
Home Office guidance says a PIN or password may be requested voluntarily, but there is no power to compel it and no offence for refusing it under this Act. The device may instead be retained and sent for technical examination.
Section 84 of the Crime and Policing Act 2026, in force since Royal Assent on 29 April 2026, is different again. At the border, a warranted customs officer with reasonable grounds to suspect a person is carrying a device storing child sexual abuse images can require them to permit an approved scan and take necessary steps to enable it. Wilful obstruction can be an offence.
This power is targeted. It is not a general content-search power and should not be described as one.
Device search realities
Myth: a locked phone is "safe" and border staff always need a court order to go further. Reality: not a reliable assumption. An officer may:
- request an unlock;
- have a statutory route to require steps enabling an examination or scan;
- have power to retain the device and seek technical access.
The consequences of refusal depend on the exact power, your immigration position and the jurisdiction. They can include delay, seizure, investigation, immigration consequences or a criminal allegation, but none should be presented as automatic.
Think about what an unlocked phone reveals. It is a diary, a photo album, a map of your routines and a record of who you spend time with. Even a quick look at photos, message previews, recent calls or social apps can say a lot.
Border searches are often rapid and manual, not always forensic. That makes superficial exposure a bigger risk than many people expect.
The practical fix starts with limiting what is on the device when you travel. This is routine data minimisation, not hiding or destroying evidence. Two easy wins:
- Use a travel device with only the apps and files the trip needs, so less unrelated personal information is on view.
- Turn off lock-screen message previews, so notifications do not expose anything while the device sits on a desk or in an officer's hand.
Myth: deleted means gone. Reality: on phones and laptops, deleted files may be recoverable until overwritten. Some border agencies use forensic tools that recover recently deleted data; others simply browse what is visible.
- Worried about a quick manual search? What is currently accessible matters most.
- Expecting forensic analysis? The device's encryption design and its current state (locked or unlocked) become critical.
Biometrics vs passwords
Fingerprint and face unlock are quick to use, and quick to compel. An officer can ask you to look at a camera or put a finger on a sensor.
Some jurisdictions treat that differently from asking you to speak a passcode, because the law distinguishes providing a biometric from revealing knowledge in your mind. The distinction is not universal and can be contested, but in practice biometrics are easier to enforce in the moment.
There is no sound UK rule that passcodes can always be refused, or that they must always be supplied. It depends on the regime:
- 2025 immigration-device power: published guidance makes disclosure voluntary.
- Targeted 2026 scan power: a person can be required to take steps necessary to permit the scan.
- Schedule 7 and Schedule 3 examinations, and a later disclosure notice under the Regulation of Investigatory Powers Act 2000, are separate legal regimes with their own duties and offences.
If the stakes are serious, ask which power is being used and seek a lawyer familiar with that regime. Do not lie, destroy material or obstruct an officer.
A practical compromise: use a long passcode and disable biometric unlock before crossing a border. On many phones, restarting the device or using the power-button sequence forces a passcode on the next unlock.
That does not make you immune to requests to unlock. It does cut the risk of accidental or coerced biometric unlocks, and it tells you clearly when the device has been unlocked, which is useful for your own awareness.
Travel devices
A "travel device" is a phone or laptop set up specifically for a trip: a spare device, or your usual one with a separate user account and minimal data. Carry what you need and no more.
- Conference trip: a clean laptop with the presentation, relevant emails and access to work systems through secure remote login.
- Family holiday: maps, travel bookings and a small selection of photos.
There are trade-offs. You lose personalised settings and offline access to everything you normally carry, and a misconfigured device can lock you out while you are away.
If you use one, set it up fully and test it before you travel, and make sure you can recover it if it is lost or seized. Keep recovery codes or secondary authentication methods somewhere you can reach without the device itself.
Mistake one: assuming fewer files means "clean". Many apps sync large amounts of data once you sign in; email, cloud storage and messaging apps can pull down full histories within minutes. To limit exposure:
- use web access with limited caching; or
- use separate accounts with restricted data. A separate account used only for the trip can significantly reduce what is visible if the device is examined.
Mistake two: forgetting the browser. Saved passwords, history and open tabs can reveal a great deal, even on a minimal device. Use a browser profile that does not sync across devices, and clear history before travel. Not perfect, but it cuts the incidental information on show in a quick inspection.
Cloud access after seizure
Seizing a device is not necessarily the end of access. If it is already unlocked, officers may reach cloud services through logged-in apps. Even if it is locked, cloud data may be reachable by other means, including legal requests to service providers.
That is why even a minimal travel device can expose more than expected: it may be a key to much larger stores of data.
Cloud accounts can be protected several ways, but none is perfect. Multi-factor authentication (MFA) stops remote logins, yet on an unlocked device the second factor may already be there:
- app-based MFA can be read directly on the device;
- SMS codes can arrive on the same phone;
- security prompts can be approved with a single tap.
Hardware security keys offer stronger separation, but they can also be requested during an inspection if you carry them.
Two practical mitigations:
- Separate accounts by purpose. Keep personal photos in one account and work documents in another, and only sign into what the trip needs.
- Use "just in time" access. Log in when needed, then sign out and remove the app. Inconvenient, but it shrinks the window in which a seized device gives immediate access to your cloud data.
Watch for offline copies kept by default, such as email clients that download whole mailboxes and file-sync apps that store local copies. Set them to cache only recent items, or use web-only access. That does not remove the risk (the service still holds the data), but it reduces what is directly accessible from a seized device.
Post-inspection hygiene
After a device has been searched or out of your control, treat it as potentially modified. No need to panic or assume the worst, but there are sensible steps.
If you unlocked it under observation, change important passwords afterwards. This helps even if nothing was tampered with, because you cannot know what was seen or recorded.
Then check your accounts:
- see which accounts are still signed in;
- review recent login activity on email, cloud storage and social media (most have a "recent activity" view of new logins and devices);
- revoke anything unfamiliar and update those passwords;
- enable or reset MFA, especially if you suspect backup codes or tokens were copied.
Next, look for configuration changes you did not make: new device management profiles, unknown VPNs, apps you did not install. On phones, check system settings. On laptops, review installed applications and browser extensions.
If you cannot account for a change, the safest route is often a full wipe and reinstall of the operating system, restoring only from backups you trust. It is time-consuming and not always necessary, but it is the only way back to a known-good state if you suspect tampering.
Finally, know your own tolerance for disruption. Some travellers will reset thoroughly after any inspection; others accept the risk and do routine checks. Make that choice before you travel, not under pressure. Knowing what you will accept matters as much as any technical measure.
Official sources
- Home Office codes for Schedule 7 and Schedule 3 examination powers at ports.
- Home Office guidance on the Border Security, Asylum and Immigration Act 2025 device powers.
- Crime and Policing Act 2026 explanatory notes on the targeted border scan power and the Home Office factsheet.
Do this now
- Turn off message previews on your lock screen.
- Learn the button sequence (or restart) that disables biometric unlock on your phone, and practise it once.
- Before your next trip, sign out of any account the trip does not need.
- Store your recovery codes somewhere you can reach without your phone.