Foundations and threat modelling
The short version
- Start with three questions: what is valuable, who might want it, and how could they get it?
- Match protection to reality, not to worst-case horror stories. A landlord and a protest organiser need different things.
- Every protection has a cost. Trade-offs are decisions, not failures.
- Plan for the inevitable mistake. Limit the damage rather than hoping nothing goes wrong.
Before picking tools, changing habits or arguing about rights, work out what you are defending, who might want it, and what protecting it really costs.
That is the foundation of privacy and security. It is also the foundation of sensible decisions about speech and personal freedom in a digitally monitored world.
What is a "threat model" in ordinary life?
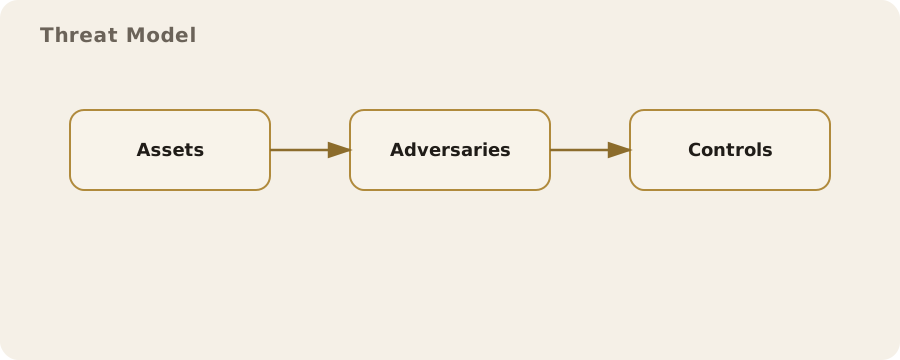
A threat model is a practical description of what could go wrong, how, and what you would lose. It is not a list of worst-case horrors. It is a way of matching protection to reality.
What "going wrong" looks like depends on who you are:
- A small business owner: a data leak, lost customers and a fine from the Information Commissioner's Office.
- A teenager: a private photo turning up in a group chat.
- A protest organiser: a phone seized and contacts exposed.
Threat modelling starts with three simple questions: what is valuable, who might want it, and how could they get it?
- Valuable: money, identity, health information, location history, political beliefs, relationships.
- Who: a criminal, a curious employer, a hostile family member, a marketing firm, the state.
- How: obvious routes like phishing emails, or subtle ones like apps quietly collecting location data.
Assets, adversaries, and your boundaries
An asset is anything you want to protect. Some are obvious: bank accounts, devices, personal data. Others are social: your reputation, your freedom to associate, your ability to speak without being profiled. Those matter because they shape how people treat you, what opportunities you get, and whether you feel safe expressing yourself.
Adversaries are people or organisations who could use those assets against you. They differ a lot in motivation and capability:
- A scammer wants quick money and usually relies on low-effort tricks.
- A stalker may know you well and can exploit shared accounts or family plans.
- A company may want to profile you for advertising or risk scoring.
- A state body may have lawful powers to request data, but those powers have limits and oversight.
Boundaries are the lines you decide not to cross. You might accept a fitness tracker recording your heart rate but refuse to share your precise location with third parties. You might be fine on public social media but draw the line at linking your real name to a pseudonymous account. That is not paranoia; it is personal values, safety and the specific context you live in.
Context shapes risk
In the UK, the legal and cultural environment matters. Data protection law limits how organisations use personal data, and there are routes to complain. That does not mean misuse never happens.
The practical risk depends on the organisation's competence, its incentives and how sensitive the data is. A national health record is protected by strict rules, yet breaches still happen through human error.
Freedom of speech works the same way: it exists within a legal framework, and legal is not the same as consequence-free.
- You can be within your rights and still face consequences at work or socially.
- Lawful speech can be misread by automated moderation systems.
Knowing this helps you set realistic boundaries: when to be public, when to be discreet, and when to avoid leaving searchable traces.
Threat modelling by example
The landlord. Manages properties through online platforms and messaging apps.
- Assets: tenant data, rent records, their own bank accounts.
- Likely adversaries: phishing criminals and opportunistic scammers.
- Realistic mitigations: strong account passwords, two-factor authentication, careful verification of payment changes.
No military-grade security needed. Just avoid the common traps and reduce the impact of a mistake.
The nurse. Uses a smartphone at work and at home.
- Assets: private conversations, family photos, access to the hospital email system.
- Adversaries: criminals, but also employer policies enforced through device management tools.
- A practical boundary: work accounts on a separate profile or device, personal data backed up and encrypted.
The community organiser. Arranging a public meeting.
- Assets: contact lists and the identity of vulnerable attendees.
- Main adversary: possibly public scrutiny rather than a criminal.
- Mitigations: invitation-only channels, not collecting personal details unnecessarily, deciding when to use real names.
The trade-off is friction: extra effort can reduce attendance, so the organiser picks a balanced approach.
Common misunderstandings that weaken security
Myth: privacy is all or nothing. Reality: it comes in degrees. You can reduce your exposure without disappearing from the internet.
Myth: encryption makes you invisible. Reality: encryption protects what a message says, not the fact it was sent. Metadata, such as who contacted whom and when, can still be highly revealing.
Myth: only people "with something to hide" need privacy. Reality: data gets misused in very ordinary ways:
- insurance pricing based on health assumptions;
- employers making decisions from social media profiles;
- data brokers selling location trails that reveal visits to clinics or support groups.
Most people are not targets, but everyone can be affected.
Understanding how data moves
Good choices need a rough map of where data flows. Use an app and data usually goes from your device to the provider, and often onwards to analytics firms, advertisers or partners.
- Necessary data makes the service work: a delivery address, payment details.
- Optional data gets quietly collected anyway, because it is valuable to the business.
Data also sticks around:
- messages can back up automatically to cloud services;
- photos can carry embedded location information;
- browsers and operating systems keep logs for convenience, readable by anyone who gets into the device or account.
A useful mindset: assume most data you create exists somewhere else too, unless you deliberately prevent it.
Risk, friction, and the reality of trade‑offs
Every protective measure has a cost: more steps, fewer conveniences, or reduced compatibility.
- Two-factor authentication makes account takeover much harder, but adds a step at sign-in and can cause trouble if you lose your phone.
- End-to-end encrypted messaging keeps content private from the provider, but can make backups and message search harder.
Trade-offs are decisions, not failures. Perfect protection is unrealistic; the aim is a balance that fits your life. A journalist or activist might accept extra friction. Someone caring for relatives who need quick access to shared devices might not.
Failure modes and how they show up
Security usually fails in ordinary ways:
- passwords reused across sites;
- security questions based on information findable on social media;
- devices left unlocked at home or at work because it feels safe.
That is not always carelessness. It is time pressure and the pull of convenience.
So the realistic defence is to reduce the impact of the inevitable mistake:
- unique passwords and a password manager limit the damage of a breach;
- device lock screens limit casual access;
- separate accounts (banking on a different email from social media, say) slow attackers down.
None of these removes risk entirely. They change the cost and likelihood of an attack.
Trust is part of the model
Much of digital life runs on trust. You trust a phone manufacturer not to ship spyware, a cloud service not to misuse your files, a friend not to forward a private message. Some of that trust is reasonable. Some of it should be tested.
Testing trust needs no technical skills:
- read permissions before installing an app;
- check whether a service offers clear privacy settings;
- look at a company's track record of responding to breaches;
- in the UK, check whether a company handling personal data is registered with the Information Commissioner's Office.
Registration does not guarantee good behaviour, but it signals a willingness to be accountable.
Setting a personal baseline
A baseline is a set of protections that are reasonable for most people. It might include:
- keeping devices updated;
- using a password manager;
- two-factor authentication on important accounts;
- backing up data without exposing it to unnecessary parties;
- knowing how to recover when things go wrong: recovery codes stored safely, and knowing how to freeze a credit report if identity theft happens.
From there, adjust to your own threat model. Travel a lot? You might separate travel devices from home devices. Worried about workplace monitoring? Keep personal and work accounts apart and avoid employer-controlled devices for private matters. Not extreme, just ordinary risk management.
Freedom of speech and the cost of visibility
Speech is not only about legality. It is also about visibility, permanence and audience. A private message is different from a public post, even if both are lawful.
The risk is not just prosecution. It is misinterpretation, harassment or consequences at work. None of that means you should stay silent. It means deciding, consciously, where and how to speak.
Practical steps:
- use different identities for different contexts;
- leave unnecessary personal details out of public discussions;
- keep records of your own speech when you expect disputes.
These are as much about resilience as security. The digital public square is open, searchable and often unkind.
Where to go next
The foundation: know your assets, adversaries and boundaries; understand how data moves; accept that trade-offs are real. From there, make deliberate choices about tools, habits and how visible you want to be. This is not about perfection. It is about clarity.
Do this now
- Answer the three questions for yourself: what is valuable, who might want it, how could they get it? Five minutes, on paper.
- Turn on two-factor authentication for your main email and your bank, if it is not already on.
- Check whether your banking uses the same email address as your social media. If so, note it as something to separate.